


Every online transaction, message and government record depends on encryption that assumes certain maths problems are too hard for any computer to solve quickly. Quantum computing challenges that assumption. Quantum computing and encryption are now discussed together across boardrooms and government guidance alike, because a sufficiently powerful quantum computer could eventually break the RSA and ECC encryption that protects most of today’s digital infrastructure.
This is not a distant academic worry. The UK’s National Cyber Security Centre (NCSC) has already published a national migration timeline running to 2035, NIST finalised its first set of quantum-resistant encryption standards in August 2024, and Google’s own researchers have recently cut their estimate of the hardware needed to break RSA-2048 by a factor of twenty. This guide sets out why quantum computing and encryption interact the way they do, what the UK’s regulators expect organisations to do about it, and a practical roadmap for getting ready before the risk becomes urgent.
Table of Contents
Why Quantum Computing Poses a Real Risk to Modern Cryptography
Most of the internet’s security relies on a small number of mathematical problems that classical computers cannot solve within a useful timeframe. Quantum computers change that equation for certain types of encryption, which is why quantum computing and encryption have become such a pressing pairing for security teams to understand.
Shor’s Algorithm and the Threat to RSA and ECC
RSA and Elliptic Curve Cryptography (ECC) both rely on problems that are, for a classical computer, practically impossible to reverse within a useful timeframe: factoring huge numbers, in RSA’s case, and solving discrete logarithms on elliptic curves, in ECC’s. In 1994, mathematician Peter Shor showed that a sufficiently large quantum computer could efficiently solve both problems, reducing what would take classical computers longer than the age of the universe to a matter of days. This single result is the reason quantum computing and encryption cannot be treated as separate fields of study any longer.
No quantum computer today comes close to that scale. Google’s own research, published in May 2025, estimated that breaking a 2048-bit RSA key would need a quantum computer with around one million noisy qubits running continuously for about a week, itself a twenty-fold reduction from the twenty million qubits Google had estimated back in 2019. Today’s largest quantum processors hold only hundreds to a few thousand qubits, so the hardware gap remains substantial.
What has changed is the direction of travel: each new algorithmic improvement has shrunk the resource estimate, not grown it, and that trend is exactly why standards bodies are treating this as a live planning issue rather than a distant hypothetical. This is also why “harvest now, decrypt later” has become such a common phrase in cybersecurity circles: an attacker doesn’t need a working quantum computer today to benefit from one in the future. They only need to capture encrypted traffic now and wait.
Symmetric Encryption: Why AES Survives Better
Not all encryption is equally exposed. Symmetric algorithms such as AES are affected differently, because the best-known quantum attack against them, Grover’s algorithm, only offers a quadratic speed-up rather than the near-total break Shor’s algorithm delivers against RSA and ECC. In practice, this means AES-256 remains considered quantum-resistant, retaining an effective 128-bit security margin even against a quantum attacker, while AES-128 drops to a 64-bit margin that is considered too thin for long-term protection.
Businesses using modern encryption methods for data at rest are generally in a stronger position than those relying solely on RSA or ECC for key exchange and digital signatures, which is precisely the area where quantum computing and encryption standards are now converging on new, quantum-resistant algorithms.
The Harvest Now, Decrypt Later Threat
Understanding why data captured today matters tomorrow requires looking past the headline question of when a working quantum computer might arrive, and towards which data types are actually at risk in the meantime.
Attackers, including state-sponsored groups, are already storing intercepted encrypted communications with no expectation of reading them immediately. The value only appears once decryption becomes feasible, which is why security agencies on both sides of the Atlantic now treat today’s encrypted traffic as a future liability rather than a solved problem. This makes long-lived data especially exposed: intellectual property, health records, government communications and financial data that needs to remain confidential for a decade or more.
A message that only needs to stay secret for a few days carries very little harvest now, and decrypting it later risks. A patient record, a state secret, or a long-term commercial contract carries a great deal of value, because the value of the underlying data hasn’t diminished by the time a quantum computer becomes capable of reading it.
Financial services, healthcare and government are the three sectors most exposed to this specific risk, given how long they are legally or commercially obliged to retain sensitive records. The NCSC has gone so far as to advise that organisations should simply assume that some of their sensitive encrypted data is already being collected for future decryption, rather than treating the risk as hypothetical.
Organisations handling this kind of long-life data have the strongest reason to start planning their migration away from RSA and ECC and towards quantum-resistant data encryption methods, rather than waiting until quantum computers actually exist at scale. By the time that happens, any data captured today will already be exposed, which is the central reason quantum computing and encryption need to be planned for together rather than treated as separate problems.
The Global Response: NIST’s Post-Quantum Standards
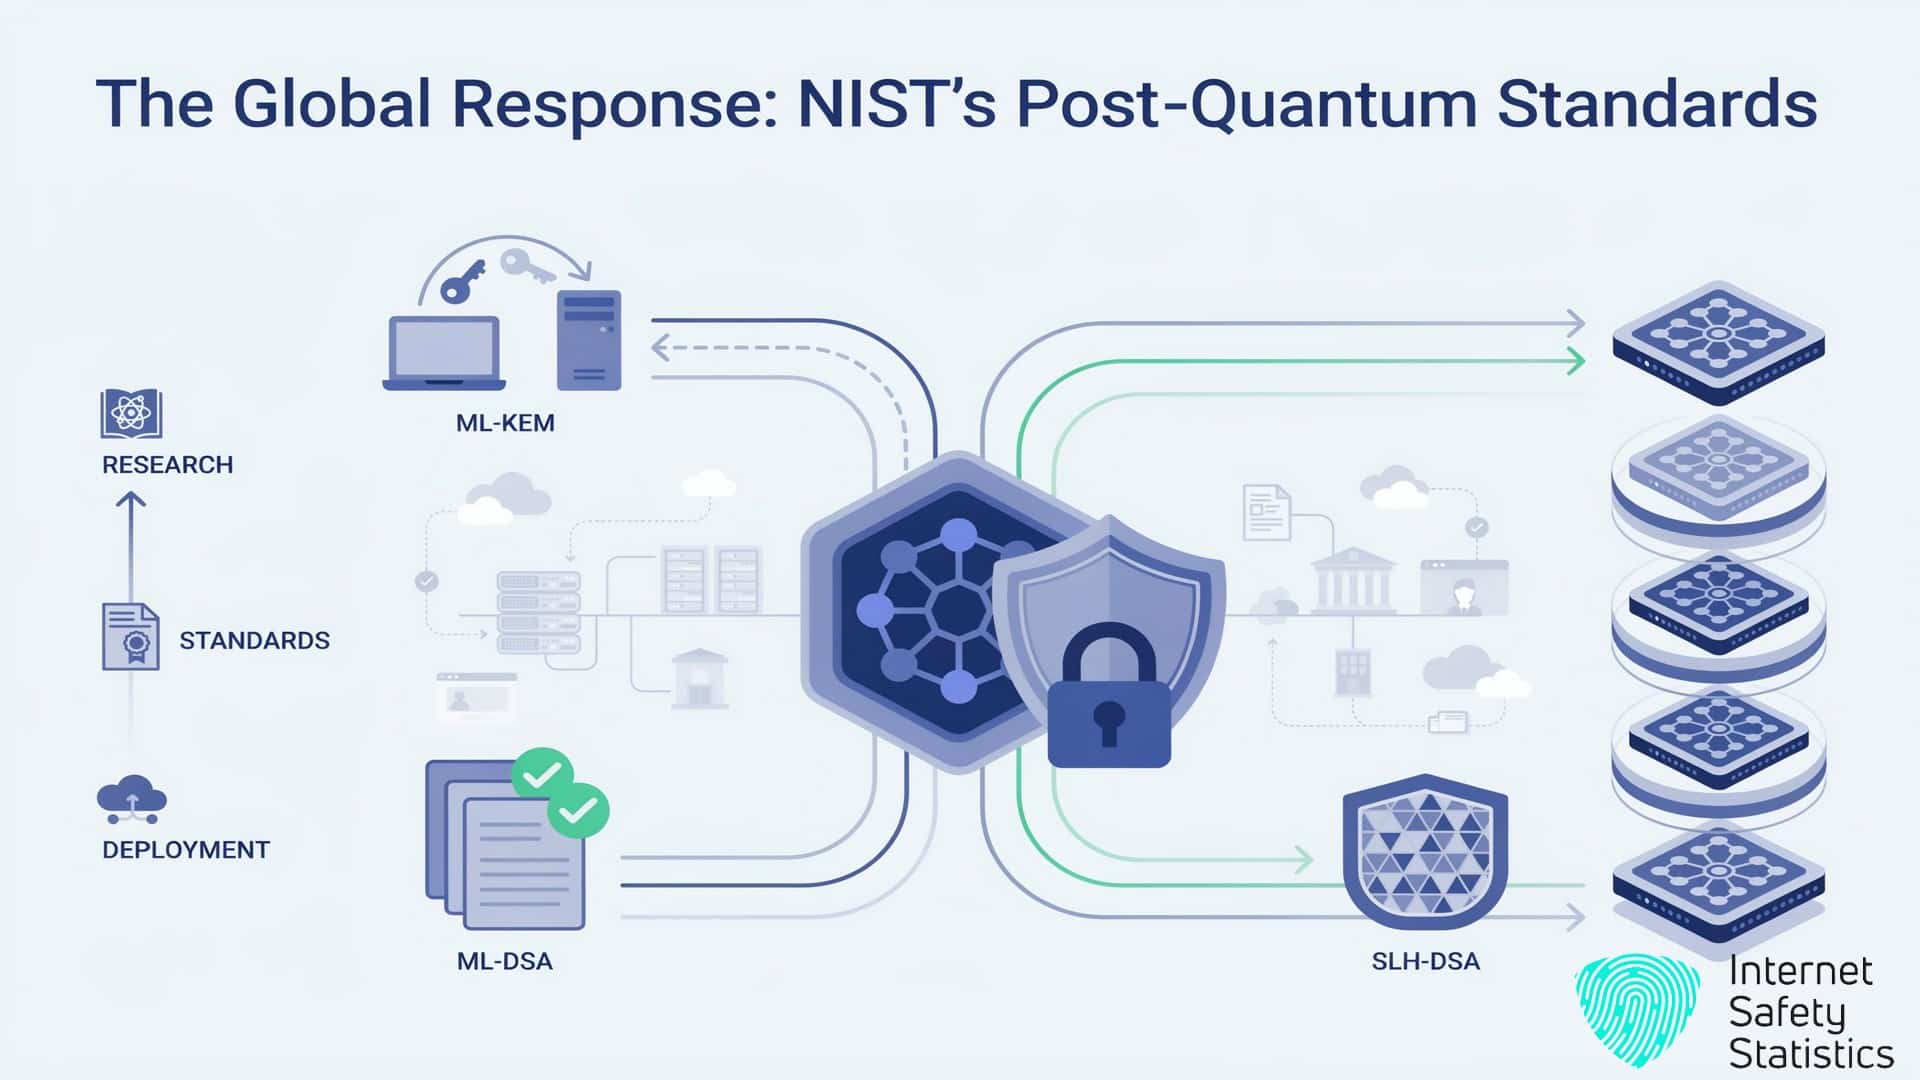
Understanding the threat only matters if there’s a credible answer to it, and the response to quantum computing and encryption risk has moved from research into published, usable standards over the past two years.
ML-KEM, ML-DSA and SLH-DSA Explained
In August 2024, the US National Institute of Standards and Technology (NIST) finalised three post-quantum cryptography standards after an eight-year public evaluation process that began in 2016. FIPS 203 specifies ML-KEM (built on the CRYSTALS-Kyber algorithm), a key encapsulation mechanism designed to replace RSA and Diffie-Hellman key exchange. FIPS 204 specifies ML-DSA (built on CRYSTALS-Dilithium), the primary replacement for RSA and ECDSA digital signatures, offering smaller signature sizes and faster verification than earlier lattice-based proposals.
FIPS 205 specifies SLH-DSA (built on SPHINCS+), a hash-based signature scheme that rests on a different mathematical assumption entirely, giving organisations a fallback if any weakness were ever found in the lattice-based approach that underpins the other two. A fourth standard, FN-DSA, based on the Falcon algorithm, remains in draft, and NIST added a further key encapsulation algorithm, HQC, to its standardisation programme in March 2025 to provide additional algorithm diversity.
These algorithms are not theoretical. NIST has said organisations should begin migrating to them now, and browser vendors, cloud providers and hardware security module manufacturers have already started shipping support for hybrid classical and post-quantum key exchange, meaning traffic is protected by both a traditional algorithm and a post-quantum one simultaneously during the transition period.
In February 2025, Google added quantum-safe digital signatures to its Cloud Key Management Service, and several major browsers now negotiate hybrid post-quantum key exchange by default for supported connections. Momentum is also building on the hardware side: that same month, Microsoft unveiled an early quantum chip design intended to scale to far larger qubit counts over time, a reminder that the gap between today’s quantum computing and encryption research and tomorrow’s working hardware keeps narrowing rather than widening.
NCSC Guidance: The UK’s Roadmap to 2035
Where the NIST standards answer the “which algorithms” question, the NCSC’s own guidance answers the “by when, and how” question for UK organisations specifically, and it is this UK-specific detail that most quantum computing and encryption content aimed at a US audience overlooks entirely.
The Three-Phase Migration Timeline
In March 2025, the NCSC published its Timelines for Migration to Post-Quantum Cryptography, setting a national roadmap in three phases. By 2028, organisations should complete a full discovery exercise, identifying which services and infrastructure depend on vulnerable cryptography, and build an initial migration plan. Between 2028 and 2031, the guidance calls for early, high-priority upgrades to the systems and data most at risk, refining plans as PQC products mature.
By 2035, the NCSC expects complete migration to post-quantum cryptography across all systems, services and products, with a small tail of harder-to-reach legacy technology accepted as an exception rather than the rule. This timeline is the clearest signal yet that quantum computing and encryption planning have moved from a research question to a national infrastructure programme. The guidance aligns with the NIST standards, recommending ML-KEM-768 or higher as a baseline for UK organisations, a slightly lower bar than the ML-KEM-1024 mandated for US national security systems under the NSA’s separate Commercial National Security Algorithm Suite.
The NCSC has been explicit that this is not solely a large-enterprise concern. For many small and medium-sized businesses, migration will happen largely automatically as software, cloud services and hardware vendors update their products in the ordinary course of business, though relying entirely on vendors without any internal awareness of the timeline is a risk of its own. Since 2024, a growing number of vendors have had PQC implementations validated through NIST’s Cryptographic Algorithm Validation Program, and several major browsers already support hybrid post-quantum key exchange in their communication stacks.
UK GDPR and the “State of the Art” Obligation
Article 32 of the UK GDPR requires organisations to implement security measures that are appropriate to the risk, taking into account the state of the art. The Information Commissioner’s Office has confirmed that assessing whether an encryption method meets this bar involves considering whether it aligns with recognised standards such as FIPS 140-3 and remains fit for purpose as technology and threats evolve. Encryption itself is not mandatory under UK GDPR, but where it is used, it needs to reflect current practice rather than a fixed choice made years ago and never revisited, which is exactly where quantum computing and encryption obligations start to overlap with everyday compliance work.
As post-quantum standards become established and widely available across mainstream software and cloud platforms, an organisation that has made no plan to move away from RSA or ECC for long-life sensitive data may find it harder to demonstrate that its security measures reflect the current UK GDPR state-of-the-art requirement, particularly once PQC-capable products become standard rather than niche. This is a compliance argument for starting the discovery work now, well before any formal deadline forces the issue.
Quantum Key Distribution versus Post-Quantum Cryptography
There are two distinct approaches to quantum-safe security, and they are often confused with one another despite working in fundamentally different ways. Understanding both is part of getting quantum computing and encryption strategy right, since choosing the wrong approach can mean investing in hardware most organisations will never need.
Quantum Key Distribution (QKD) uses the physical properties of quantum mechanics to detect eavesdropping on a dedicated communication channel, and requires specialised hardware such as fibre links or satellite connections. Post-quantum cryptography (PQC), by contrast, uses new mathematical problems believed to resist quantum attacks, and runs on existing infrastructure through an ordinary software update.
| Factor | QKD | PQC |
|---|---|---|
| Approach | Physics-based key exchange | Maths-based algorithms |
| Infrastructure | Dedicated hardware, limited range | Runs on existing networks and devices |
| Cost | High, specialist deployment | Low, software-level upgrade |
| Scalability | Limited to point-to-point links | Scales across the internet |
| NCSC position | Niche, specific use cases | Recommended for most commercial use |
The NCSC has been clear that PQC, not QKD, is the practical path for the overwhelming majority of UK businesses. QKD’s hardware requirements and limited range make it suitable for a narrow set of high-security, fixed-location scenarios, such as links between government buildings or data centres, rather than a general-purpose replacement for the encryption most organisations already rely on, including website encryption using HTTPS and RSA encryption for everyday transactions. For nearly every UK business reading NCSC guidance, PQC will be the relevant approach, and QKD can safely be treated as a specialist topic rather than a live decision.
A Practical Quantum Readiness Roadmap for UK Businesses

Migrating an entire organisation’s cryptography is a multi-year undertaking, and the NCSC’s own guidance breaks the quantum computing and encryption migration work into discrete, manageable stages rather than a single overwhelming project.
Step 1: Discover Your Cryptographic Assets
Start by cataloguing where encryption is actually used across the organisation: TLS certificates, VPNs, code signing, database encryption, backup systems and any custom-built software that handles cryptographic operations directly. Most organisations underestimate how many places RSA or ECC are quietly embedded, often in third-party software and older hardware nobody has audited in years. This discovery phase is the foundation that the NCSC expects every organisation to have completed by 2028.
Step 2: Prioritise by Data Sensitivity and Longevity
Not every system needs to move first. Data that must stay confidential for a decade or more, such as health records, legal documents and long-term commercial contracts, should be prioritised over data with a short useful shelf life. The harvest now, decrypt later risk described earlier should directly shape which upgrades happen soonest, since delaying migration on the longest-lived data carries the greatest exposure.
Step 3: Build Cryptographic Agility
Rather than swapping one fixed algorithm for another, aim for systems that can support multiple cryptographic methods and switch between them without a full rebuild. This matters because PQC standards are still evolving: HQC was only added to NIST’s standardisation programme in March 2025, and additional signature algorithms remain in draft form, so systems built with flexibility in mind will cope better with future changes than those hard-coded to a single algorithm.
Step 4: Test in Sandbox Environments
Before rolling out PQC in production, test hybrid classical and post-quantum key exchange in a controlled environment. Hybrid approaches, which run a traditional algorithm alongside a post-quantum one, let organisations gain quantum resistance without removing a proven fallback while the wider environment, including information security tooling and vendor support, continues to mature around the new standards.
The theoretical threat that quantum computing poses to RSA and ECC has moved from academic papers into published government timelines and finalised technical standards. NIST’s algorithms are ready to implement, the NCSC has set out clear UK milestones through to 2035, and UK GDPR’s state-of-the-art requirement means the compliance case for starting now will only get stronger as PQC adoption becomes routine across mainstream software and cloud services.
Organisations that begin the discovery and planning work today, rather than waiting for a firmer deadline or a headline-grabbing quantum breakthrough, will be the ones migrating in an orderly way rather than scrambling once quantum computing and encryption stop being a future risk and start being a present one.
Frequently Asked Questions
These are the questions UK IT leaders and business owners ask most often when they first encounter quantum computing and encryption as genuine planning issues rather than future problems.
Will quantum computing break current encryption?
Yes, specifically asymmetric encryption such as RSA and ECC, which rely on mathematical problems that Shor’s algorithm can solve efficiently on a sufficiently powerful quantum computer. Symmetric encryption, such as AES-256, is far more resistant and is not considered an urgent priority for replacement, which is why discussions of quantum computing and encryption tend to focus on asymmetric algorithms first.
When will quantum computers be able to crack RSA?
There’s no confirmed date. Most public estimates put a cryptographically relevant quantum computer, one capable of breaking RSA-2048 in practice, somewhere in the 2030 to 2035 window, though recent research has repeatedly lowered the hardware bar needed to get there, so this estimate could continue to shift.
Is AES-256 quantum-safe?
AES-256 is considered quantum-resistant because the best-known quantum attack against it only halves its effective security, leaving a 128-bit margin that remains impractical to break with any foreseeable quantum computer. AES-128 offers a smaller margin and is less future-proof for data that needs long-term protection.
What’s the difference between Quantum Key Distribution and post-quantum cryptography?
QKD uses the physical properties of quantum mechanics to detect eavesdropping, while post-quantum cryptography uses new mathematical algorithms that run on existing infrastructure via ordinary software updates. Most UK organisations will only ever need to plan for the latter.
What should my business do right now?
Start with a discovery exercise to identify where RSA and ECC are used across your systems, then prioritise migration planning around the data that needs to remain confidential the longest, using the NCSC’s 2028, 2031 and 2035 milestones as your planning horizon.
Does the NCSC recommend QKD or PQC?
The NCSC recommends PQC as the practical, scalable path for the vast majority of commercial organisations, with QKD reserved for a narrow set of specialist, fixed-location use cases such as government or defence infrastructure.